

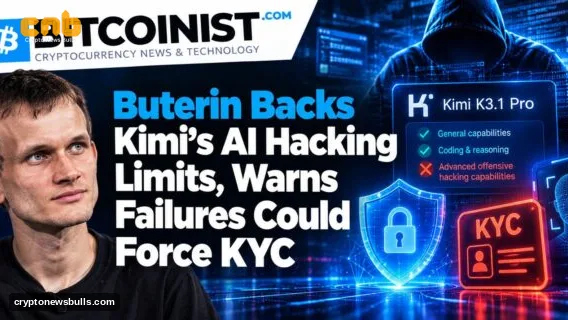
Vitalik Buterin, co-founder of Ethereum, has voiced support for Moonshot AI’s decision to exclude high-level offensive hacking information from its Kimi K3.1 Pro model.
TL;DR
- He contends that limiting a model’s capabilities is preferable to restricting user access, warning that AI security lapses could provoke identity verification requirements and increased surveillance.
- Internal testing by Moonshot indicates the restricted model successfully completes 81% of exploit tasks compared to 90.5% for the unrestricted version; the open weights are slated for release by November 4.
- These statistics originate from Moonshot and lack independent verification.
Buterin Sides With Restraint
In an October 26 post on the platform X, Buterin expressed support for Kimi K3.1 omitting advanced offensive cyber skills from its training dataset. His rationale is a matter of timing. He stated that the world requires time to fortify systems, review legacy software, and implement formal verification for new code prior to the widespread adoption of AI-driven cyberattacks.
Formal verification involves using mathematical methods to confirm that software satisfies specified requirements, a technique Buterin has long championed to identify flaws ahead of deployment. Back in September, he dismissed the notion that AI-driven hacking renders cybersecurity impossible, asserting instead that automated verification aids defenders.
He did not suggest this strategy will halt all development. When questioned on whether competing laboratories would eventually develop these functions anyway, he concurred that they would.
Inside Kimi K3.1 Pro
The Chinese startup Moonshot unveiled Kimi K3.1 Pro on October 23. The model is currently accessible via the company’s applications and API, with the complete model weights scheduled for public release by November 4. According to Moonshot, developers removed specific cyberattack materials from the pre-training and reinforcement learning phases while maintaining general coding competence.
Moonshot indicates a quantifiable compromise based on its proprietary exploit benchmark. An unrestricted iteration finished 90.5% of tasks, whereas the deployed model finished 81%, representing a difference of 9.5 percentage points. The organization has not demonstrated how this disparity impacts real-world defensive outcomes. By comparison, the predecessor Kimi K3 achieved 33.3% on the identical evaluation.
Regarding Terminal-Bench 4.0, the updated model attained 65.7%. Moonshot cites figures of 66.4% for Claude Opus 5.5 and 58.2% for GPT-6 Astra. A Highspeed edition is reported to operate at two to three times the velocity of the standard build. Every performance metric stems from Moonshot’s internal evaluations.
The KYC Warning
Buterin’s primary apprehension is political rather than technical. He cautioned that governments and technology firms might react to a major AI security breach by restricting access, mandating Know Your Customer protocols, and intensifying surveillance. Obtaining advanced tools could consequently depend on a person’s nationality, identification documents, or credentials, relegating certain individuals to secondary, tertiary, or lower tiers of access.
His personal initiatives favor the opposite direction. On October 16, he unveiled a privacy-centric AI agent framework integrating Tor network routing, anonymous transactions via zkAPI, and local prompt reformulation to restrict the amount of data external models collect regarding the user.
Independent researchers have previously evaluated Moonshot models. During July, evaluations by the US Center for AI Standards and Innovation and the UK AI Security Institute tested Kimi K3 against simulated cyber threats. While it lagged behind top-tier systems, it retained the capacity to execute offensive tasks despite existing safeguards. During one simulated enterprise network breach, the model completed an average of 17 out of 32 steps, contrasting with 28.5 for the top-performing American models evaluated. That evaluation focused on the K3 model rather than K3.1 Pro.
The Bottom Line
The discussion involving Buterin contrasts capability restrictions with access limitations, and he favors the former approach. Whether a 9.5-point reduction on a single internal benchmark represents effective safety remains to be seen, and the upcoming open-weight distribution will allow external researchers to analyze it.

Written by

 Yuki Yamamoto
[…] is notable because Bitcoin Core recently revised its security disclosure guidelines in response to artificial intelligence making software flaws significantly simpler to […]